Journal.
Research, field notes, and practical guides from the Ryvane team.
Latest writing
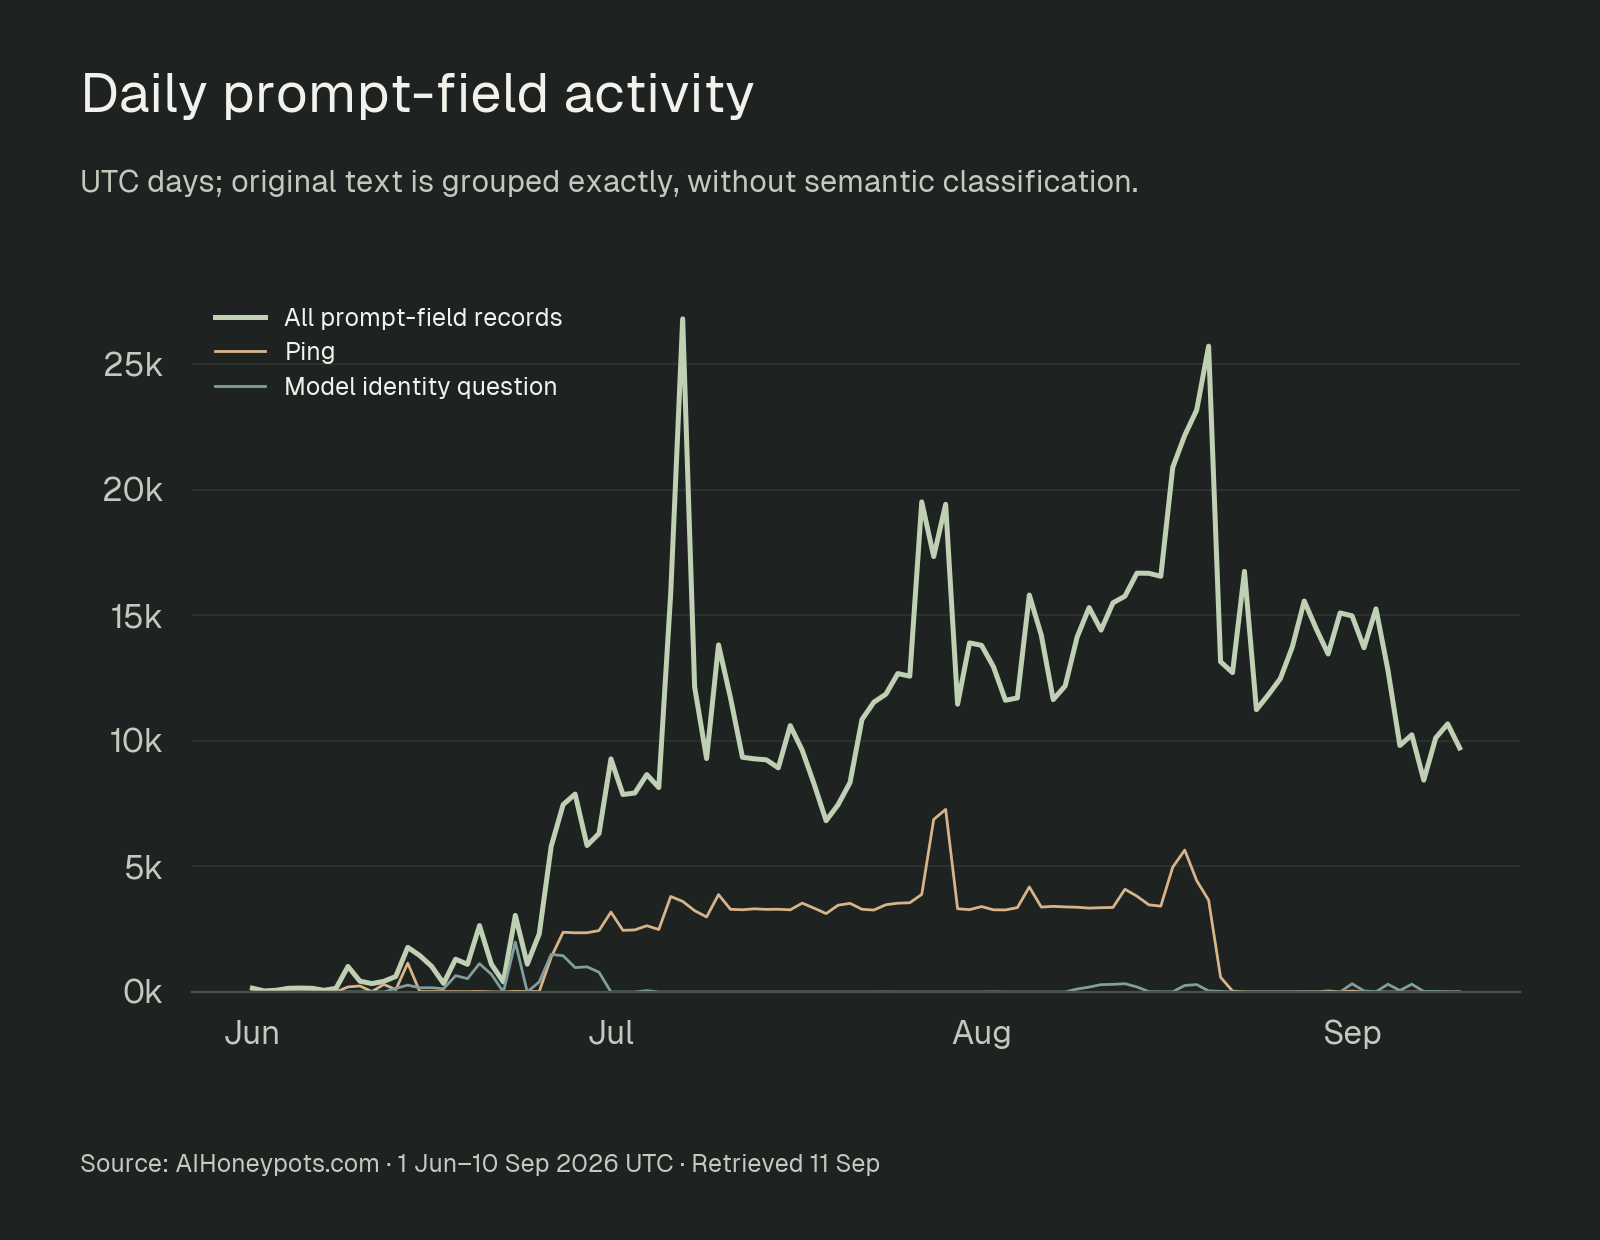
Beyond Prompt Injection: What Our AI Honeypots Are Seeing
Most AI attacks in our honeypot traffic never try to trick a model at all. They hunt for keys, fingerprint the backend, ride free compute, and ask connected tools for data. A plain-language tour of what we actually recorded from June to September 2026.
Read article
AI Honeypots: What They Are and How to Build One
A beginner's guide to honeypots: what a decoy records, how an AI honeypot differs, how to build one from the open-source Holiday Honeypot up, and how Aadesh Shinde and Eli turn the traffic into evidence you can act on.
Read article
MCP Tool Poisoning Attacks: Four Live Demos and How to Defend Against Them
A tool's description is untrusted text that your AI model reads as instructions. We demonstrate four working tool poisoning attacks against real MCP servers (description injection, tool shadowing, rug pulls, and output pollution), explain why each one works, and walk through the defenses that actually hold.
Read article
Agent Memory: Build It, Break It, Secure It
Agent memory is what makes AI assistants feel useful, and it is the part almost nobody secures. A hands-on build-it, break-it, secure-it tour of working, semantic, episodic and procedural memory in LangGraph, with four real attacks (poisoning, persistent injection, cross-user leakage and extraction) and the defenses that hold.
Read article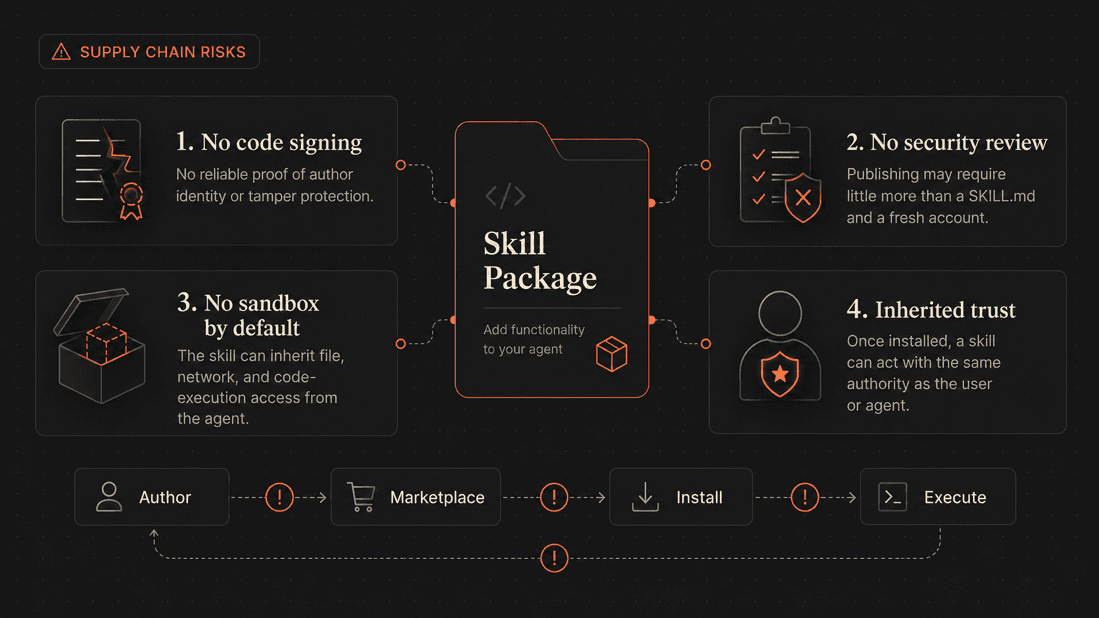
Agent Skills: Build Them, Break Them, and Secure the Supply Chain
Agent Skills turn a general agent into a specialist, but installing one extends your trust boundary to whoever wrote it. A practical tour of how skills work, how malicious skills abuse that trust through direct and indirect injection, excessive tool grants, and supply-chain drift, and how to review, sandbox, and scan them.
Read article
Joining the Claude Partner Network as a Select partner
Ryvane is a Select partner in the Claude Partner Network Services Track. A short note on what this partnership means for the research and training work we set out to do.
Read articleIntroducing Ryvane, and What We're Building Next
Why I moved from breaking traditional systems to building an AI security company. A note on what Ryvane is, the gap Ryvane Academy is built to close, and what comes next.
Read article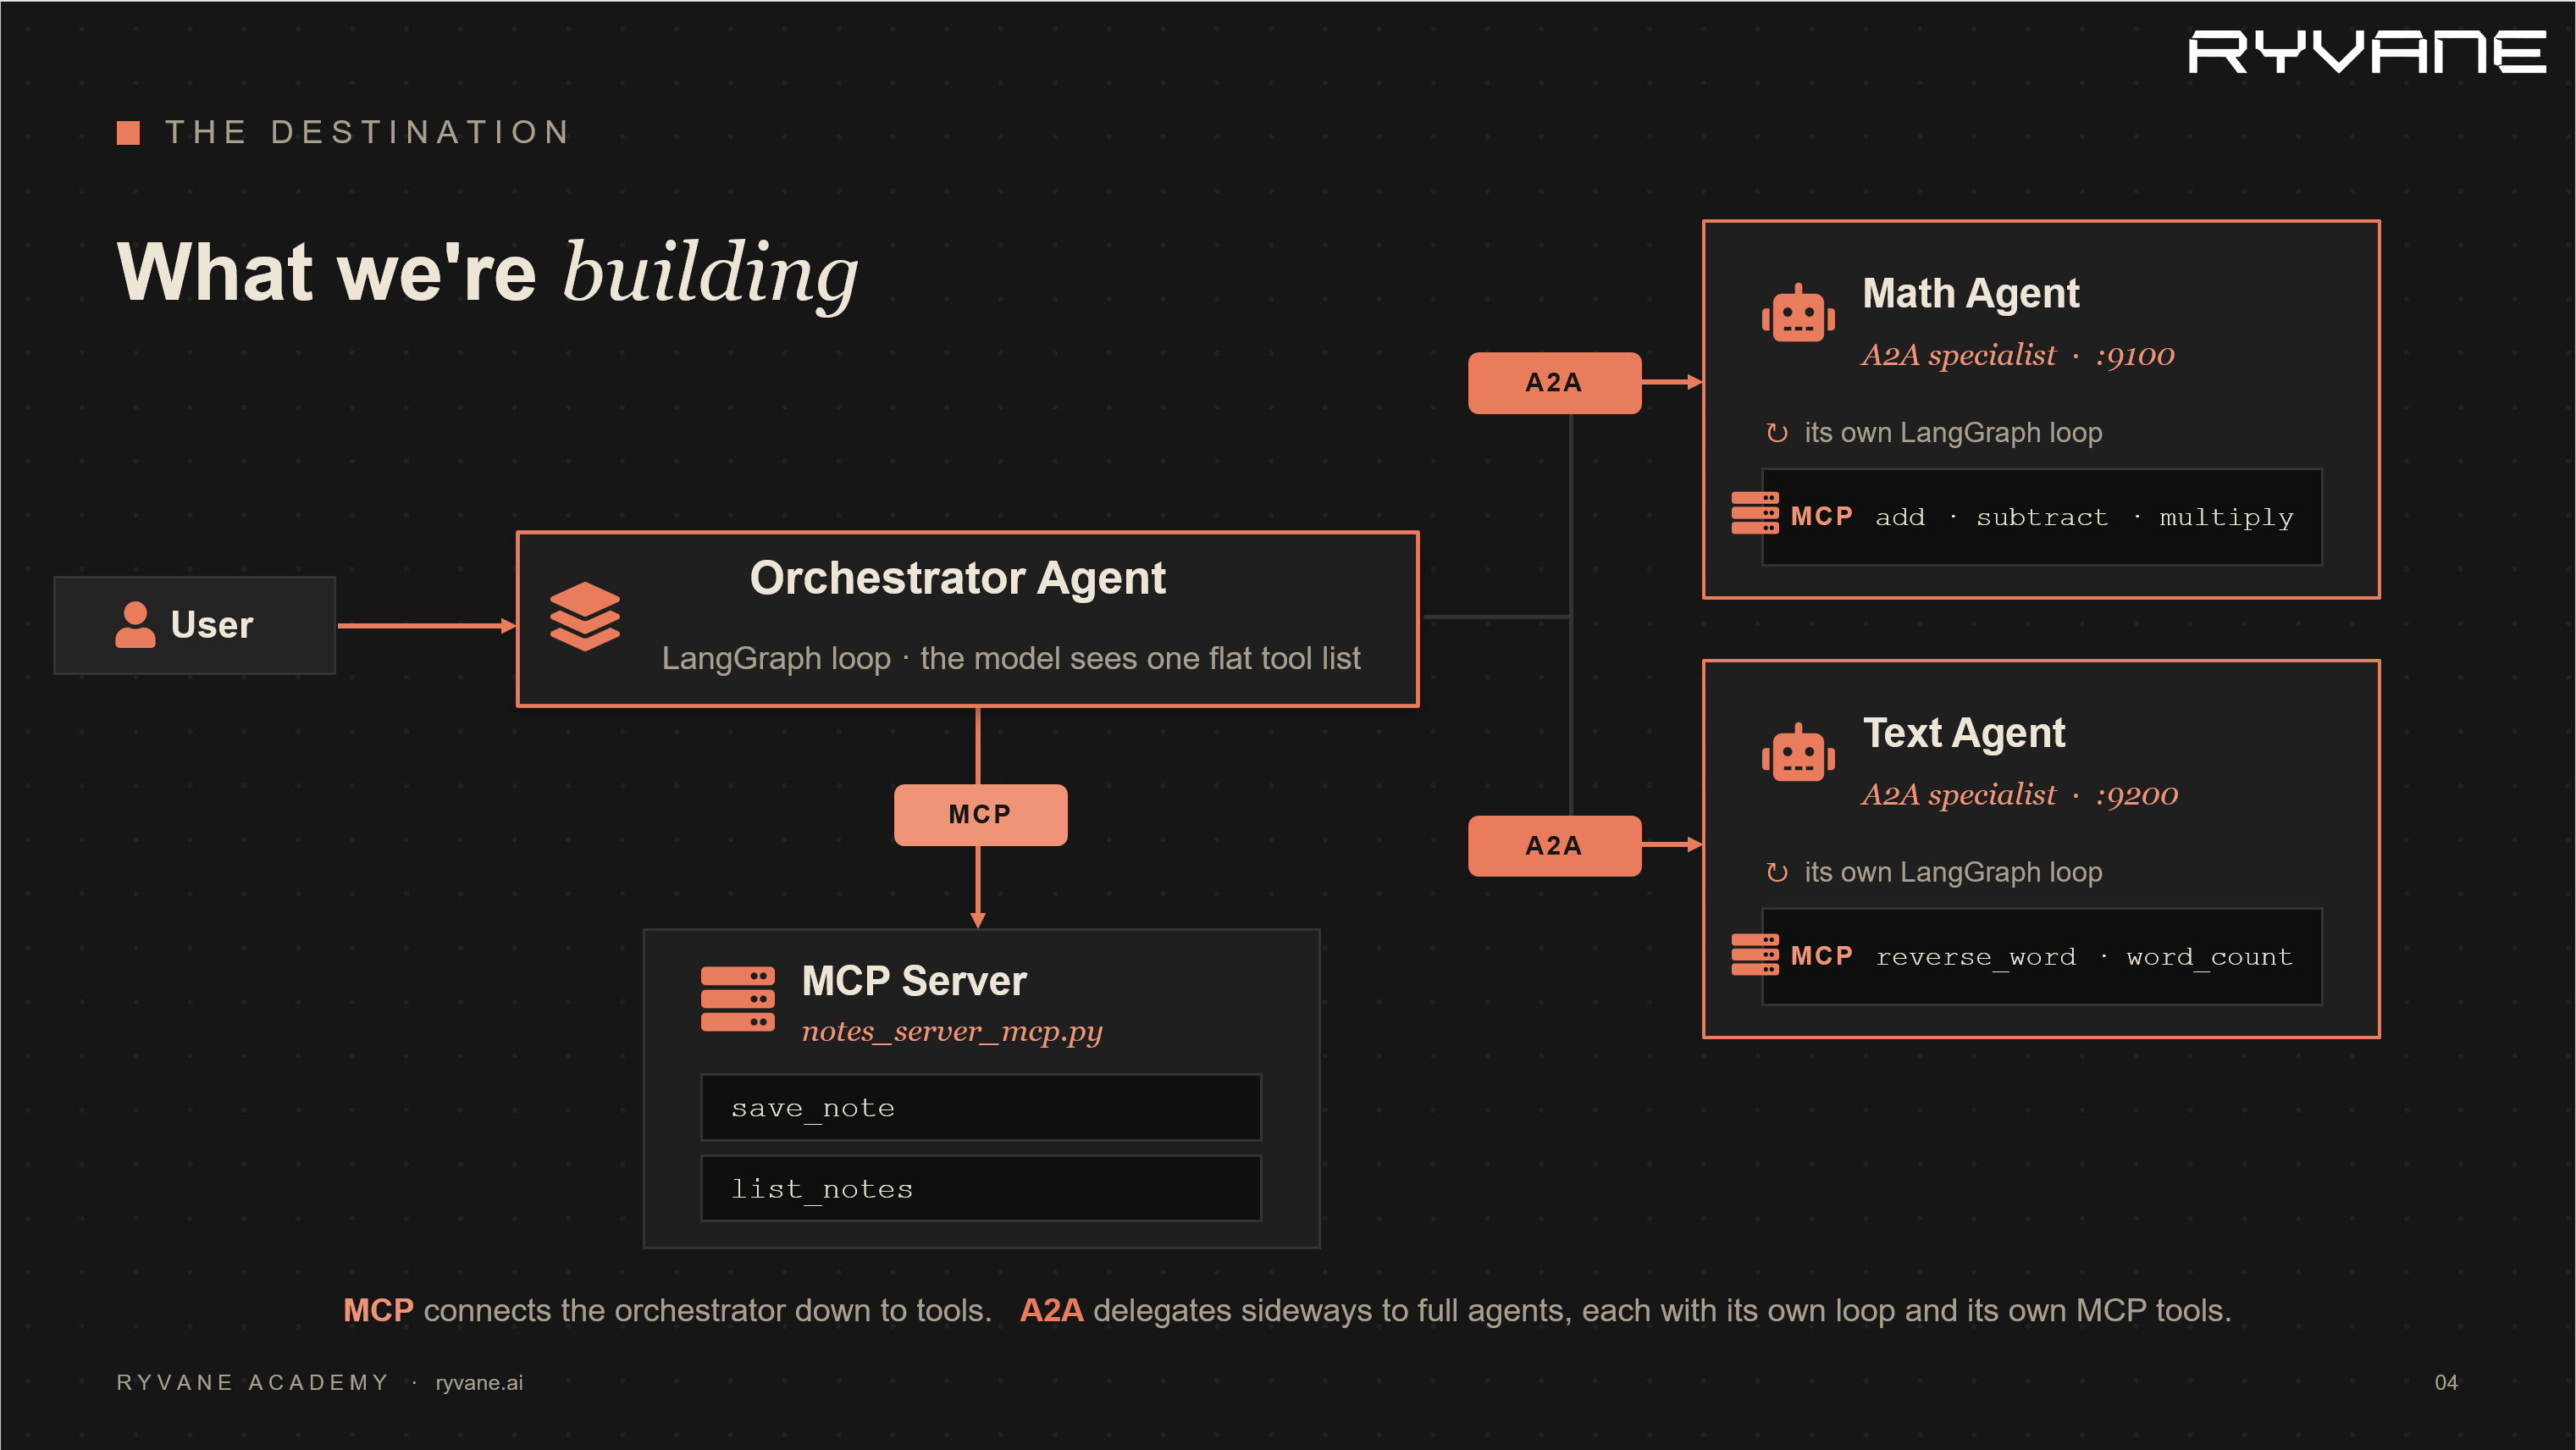
Building AI Agents using LangChain, MCP and A2A
Most agent tutorials cover one piece in isolation. This guide stitches LangChain, LangGraph, MCP, and A2A into one practical system: an agent loop that calls external tools and delegates work to specialist agents over the network.
Read articleNever miss an AI breakthrough
Join our newsletter to never miss the latest AI Security Research, News, and tips delivered straight to your inbox.
No spam. Unsubscribe at any time.